Security that passes audit
and survives reality
A pragmatic ISO 27001 and GRC practice for Canadian and North-African SMBs. We scope your ISMS, write the policies your team will actually follow, and walk you through certification without the theatre.
Six programs, one methodology — scoped to your risk, not a template.
We don't sell platforms. We write the documentation, run the workshops, build the evidence, and sit beside your team in the audit room.
Gap & maturity assessment
A structured, four-week review against ISO 27001:2022 and your sector's baseline. Findings, remediation plan, and effort estimate.
- Interviews & evidence walk
- Control-by-control scoring
- Prioritized 12-month plan
ISO 27001 implementation
End-to-end program: scope, risk methodology, SoA, Annex A controls, internal audit, and management review — through Stage 2 certification.
- Scope statement & context
- Risk register & treatment plan
- Certification shepherding
GRC program build
Policy library, control matrix, and evidence workflows in your GRC tool of choice — Vanta, Drata, or a properly-configured Odoo.
- 22 core policies · EN/FR
- Control-to-evidence mapping
- Tool selection & setup
Enterprise risk management
A risk register your board will read. Quantitative where we can (FAIR), qualitative where we must, reviewed on a quarterly cadence.
- Risk taxonomy · tolerance
- Quarterly risk committee
- Third-party & vendor risk
Fractional CISO
A senior security leader on your exec team for 4–10 days a month. Strategy, board reporting, incident response, and vendor reviews.
- Board & exec reporting
- Incident-response lead
- Audit & questionnaire owner
Security awareness & training
Programs your team completes on purpose — scenario-driven, bilingual, reinforced with phishing exercises that match your threat model.
- All-staff curriculum · EN/FR
- Role-based modules · dev / finance
- Phishing cadence & reporting
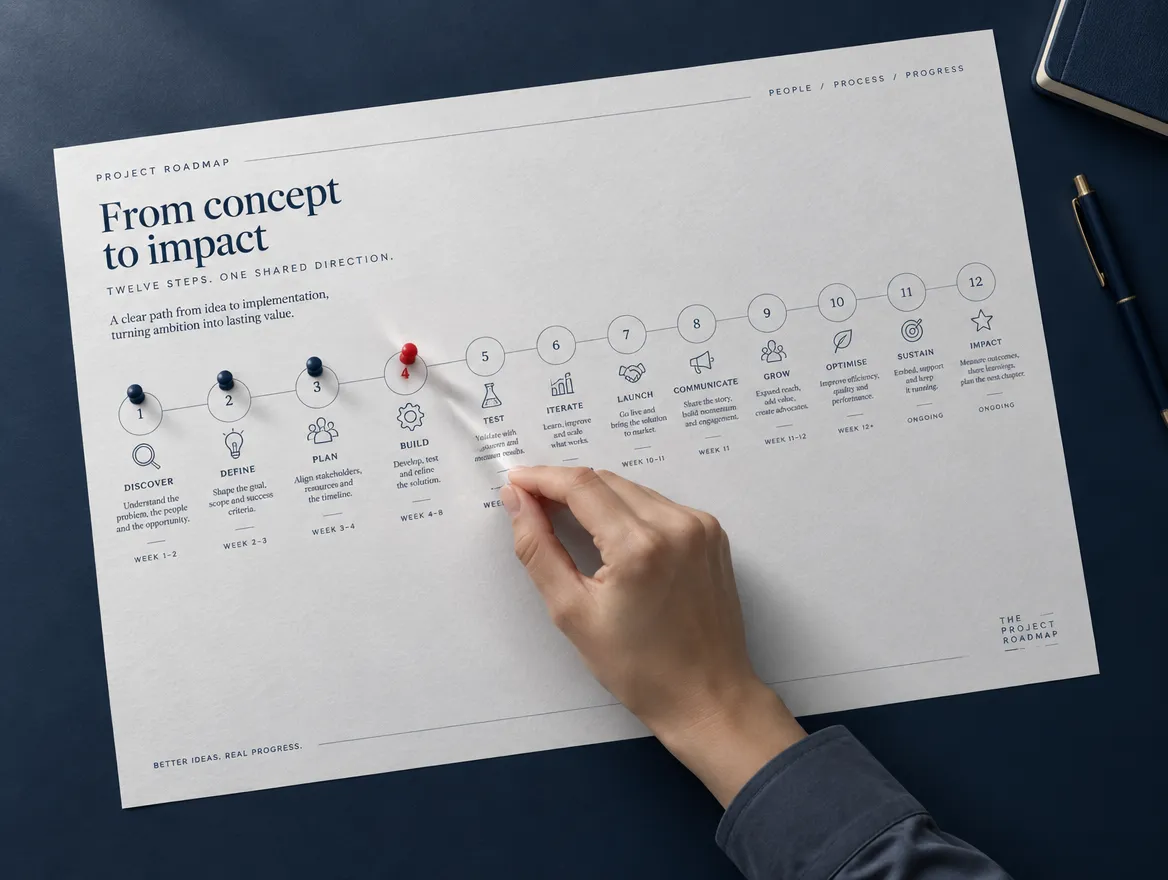
From gap assessment to certificate, in twelve months.
A predictable cadence. Each phase has a written deliverable, a signed-off exit criterion, and a clear owner on your side. No surprises at the audit.
Gap & scope
ISMS scope statement, stakeholder map, context of the organization, interested parties.
Risk register
Risk methodology, asset inventory, threat library, scored register with treatment plan.
SoA & policy
Statement of Applicability, 22 core policies, standards and procedures — all signed off.
Control rollout
93 Annex A controls implemented with owners, cadence, and evidence workflows. You are here.
Internal audit
Independent internal audit, nonconformity register, management review, corrective action.
Certification
Stage 1 readiness audit, Stage 2 certification audit, closing NCs, certificate issued.
Four control themes, ninety-three controls.
The 2022 revision consolidated 114 controls into 93 across four themes. We map each to an owner, a cadence, and a specific piece of evidence — not a paragraph of prose.
Organizational controls
Policy, roles, supplier relationships, threat intelligence, information classification.
People controls
Screening, terms of employment, awareness training, disciplinary process, remote work.
Physical controls
Perimeters, entry, equipment, clear-desk, secure disposal, cabling and utilities.
Technological controls
Access, crypto, logging, vulnerability mgmt, secure dev, backups, network security.
We've shipped the thing, not just diagrammed it.
Our security practice sits next to the team that ships websites and runs Odoo implementations. Our policies account for how your company actually builds and operates — not how a checklist imagines it.
Operators first, auditors second
Every lead is a practicing engineer, SRE, or sysadmin before they became a GRC consultant. Your controls will hold up to an auditor because they hold up to reality.
EN, FR, and Arabic — natively
Policies and training materials delivered in the language your team speaks. Critical for Québec (Law 25), Morocco, and multinational teams with regulated LOBs.
Your ISMS, not ours
We don't drop a 400-page template. We write a scope that matches your business, your risk appetite, and your audit pressure — and nothing more.
ISO 27001 · SOC 2 · Law 25 · PCI
Most clients need one framework loud and two frameworks quiet. We map once and satisfy all of them — without writing three sets of policies.
Year-one support built in
Certification is a milestone, not a finish line. Our engagements include the first year of surveillance prep, quarterly risk reviews, and incident support.
Noordev delivered our ISO 27001 certification in eleven months — and, more impressively, wrote policies our engineers actually read.
Before you book.
How long does ISO 27001 certification really take?
+Twelve months is typical for a team of 20–200 starting from scratch. Smaller or better-organized teams can do it in 8–9. We publish a week-by-week plan before we start billing.
Can we do ISO 27001 and SOC 2 Type II in parallel?
+Yes, and we usually recommend it. About 85% of the work overlaps. We write one policy set, one control matrix, and one evidence workflow — then satisfy both audits from the same system.
Do you bring a GRC tool or use ours?
+Either. We're tool-agnostic: Vanta, Drata, Tugboat Logic, Sprinto, or a well-configured Odoo for clients who prefer to keep everything in one system. We'll recommend based on scale and budget.
What does the engagement cost?
+Gap assessments start at $12,000 CAD. Full ISO 27001 implementations range $85k–$180k depending on scope, team size, and whether a vCISO is included. We send a fixed-fee proposal after the assessment.
Do you handle Québec Law 25 compliance?
+Yes. Law 25 is bundled into our ISMS work for Québec clients at no extra cost — the policies, DPIAs, breach-response procedures, and consent flows map directly onto ISO 27001 Annex A.
Can you be our certification body?
+No — by design. A certification body cannot also be your implementation partner. We prepare you and recommend three accredited CBs (Schellman, BSI, ISO-based in Canada) that have worked well for our clients.
Book a 45-minute gap conversation. No sales pitch.
Tell us what you're trying to achieve — a customer requirement, a board directive, a breach response — and we'll tell you, honestly, what the next three months should look like.